Cybersecurity services you can prove.
Nexa Cyber Security delivers manual UK penetration testing, managed security monitoring, and enterprise GRC advisory—supported by OrviQ, our continuous assurance platform built for accountable governance.
Penetration Testing UK
Manual web, API, infrastructure, cloud, and mobile penetration testing with board-ready reporting and remediation re-testing.
Managed Monitoring & SOC
Continuous detection engineering, alert triage, structured incident escalation, and digital forensics for UK enterprises.
Cybersecurity & GRC Advisory
Three Lines of Defence operating design, ISO 27001, NIST CSF 2.0, DORA, and board-level risk governance.
OrviQ GRC Technology
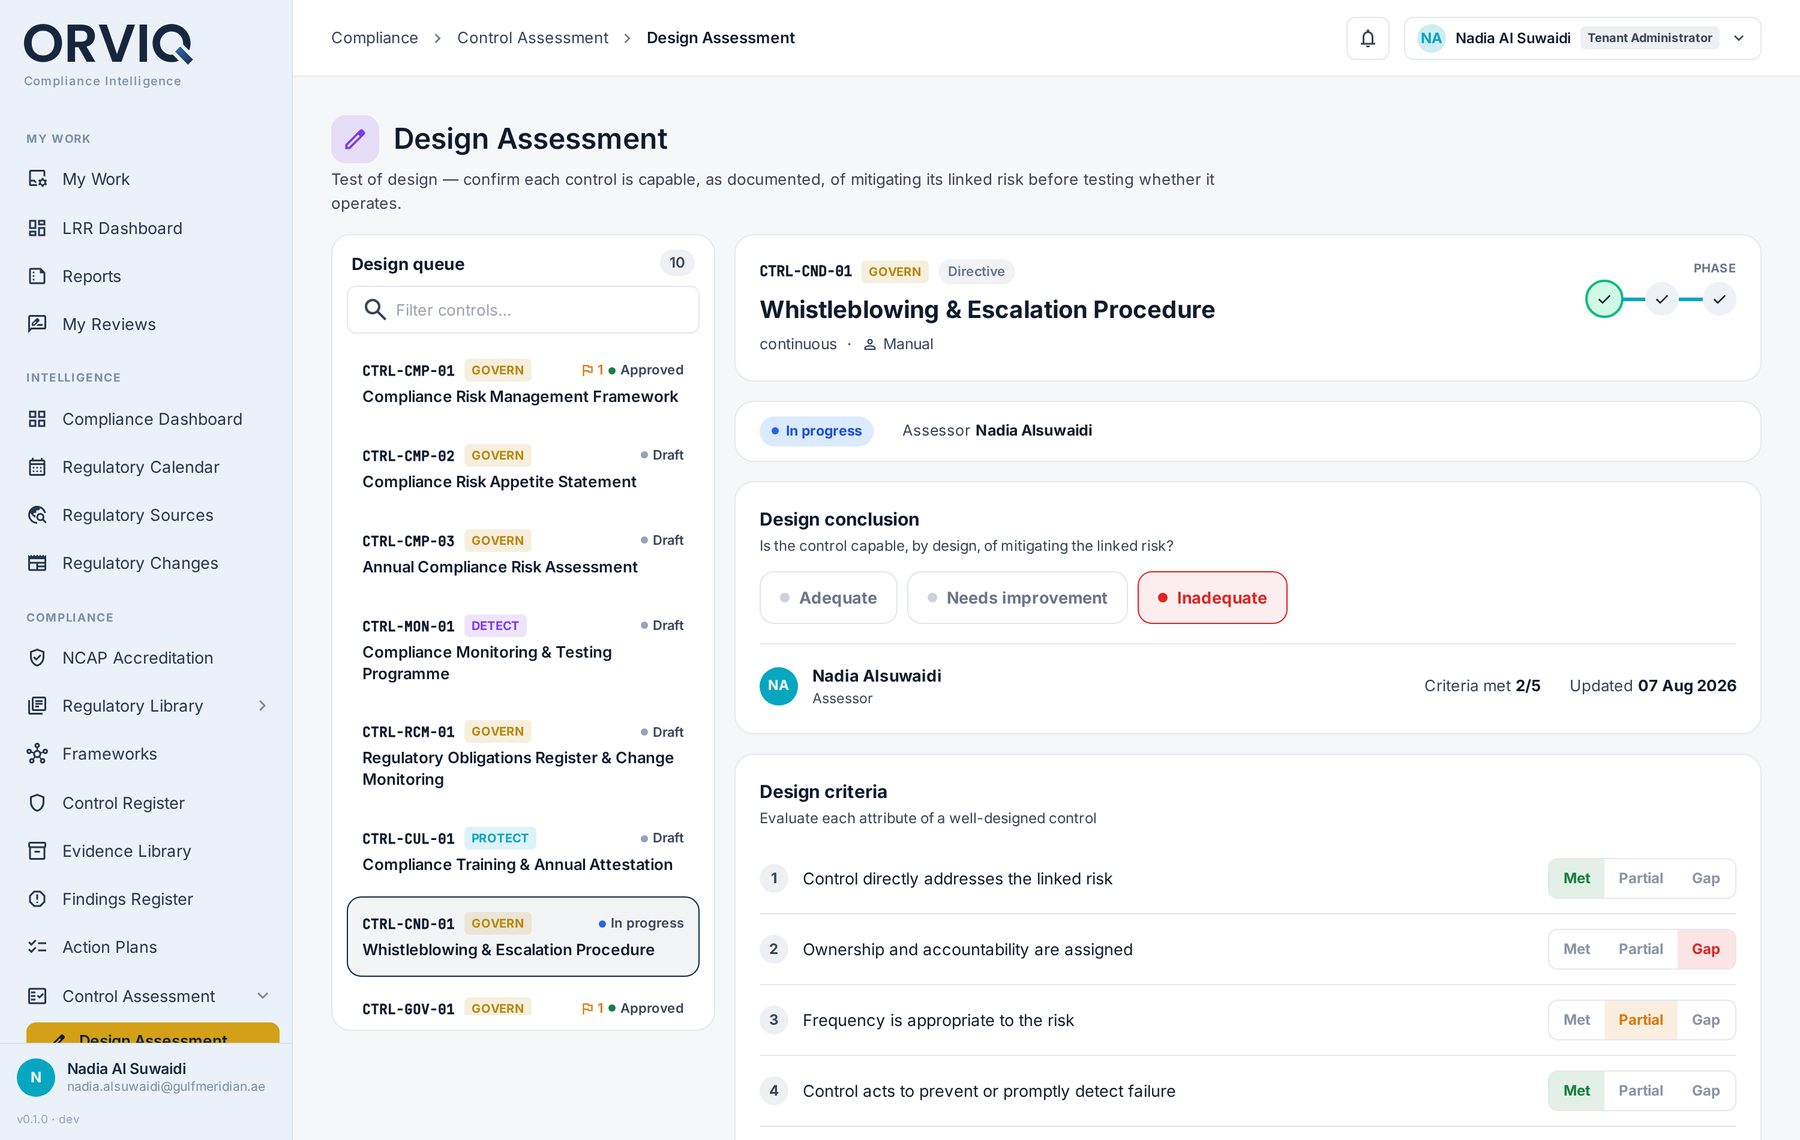
Connect penetration testing findings, controls, evidence, and continuous assurance in one governed system of record.
Three Lines of Defence (TOD) Governance
Guidelines on Compliance Risk Management · Section 1.7
3×3 Control Assurance Matrix
Penetration testing UK teams trust to test controls before attackers do.
Manual web, API, infrastructure, cloud, and mobile penetration testing delivered by Nexa Cyber Security—identifying chained vulnerabilities and providing reproducible remediation guidance.
Manual, adversary-led security assessment of enterprise web applications, microservices, GraphQL/REST APIs, and complex authentication workflows beyond automated scanner coverage.
From exploit proof to governed closure.
Every engagement delivers executive risk summaries, reproducible technical proof, and prioritised remediation guidance.
Managed security monitoring and rapid containment.
Managed SOC monitoring, threat hunting, incident response, and digital forensics delivered by Nexa Cyber Security across your cloud, identity, and endpoint telemetry.
Telemetry Ingestion
Cloud · Endpoint · Identity · SIEM
Detection & Threat Hunting
Alert Correlation · Behavioural Analysis
Containment & Investigation
Incident Isolation · Root-Cause Analysis
Control & Risk Updates
Detective Controls & Action Plans
SOC & Managed Security Services (SOCaaS)
Structured security monitoring, alert triage, and threat investigation integrated with your enterprise telemetry, cloud environments, and endpoint stacks.
Provides operational evidence for Detective controls across ISO 27001, NIST CSF 2.0, and supervisory frameworks.
Governance architecture that connects board oversight to technical reality.
Nexa Cyber Security advises UK boards, CISOs, and risk functions on Three Lines of Defence operating design, regulatory readiness, and measurable control frameworks.
Enterprise GRC & Continuous Assurance Architecture
We help risk, compliance, and security leaders architect unified governance models across all three lines of defence—connecting statutory obligations, common control registers, RCSA waves, and OrviQ technology.
Regulatory Compliance & Supervisory Readiness
Pragmatic gap analysis, Statement of Applicability (SoA) scoping, and supervisory examination preparation aligned with international control and resilience standards.
Operational Resilience & Third-Party Risk Governance
Advisory engineering to identify critical business services, define quantitative impact tolerances, map fourth-party concentration risks, and run severe-but-plausible disruption exercises.
Executive Cybersecurity Strategy & vCISO Advisory
Independent, vendor-neutral cybersecurity leadership bridging deep offensive/defensive engineering reality with board-level risk appetite, investment prioritisation, and policy governance.
 Proprietary GRC Technology by Nexa Cyber Security
OrviQ: Continuous assurance for regulated enterprises.
Developed by Nexa Cyber Security, OrviQ is our dedicated Enterprise Governance, Risk & Compliance (GRC) platform. It links statutory obligations, technical controls, penetration testing findings, and tamper-evident evidence in one governed workflow.
- End-to-End Traceability: Connect regulations, controls, evidence, and 3×3 assurance determinations without spreadsheet drift.
- Enforced Segregation of Duties: Independent second-line challenge and SHA-256 evidence freshness gates.
- Dedicated Product Site: Full platform documentation, interactive walkthroughs, and architecture specifications are hosted at orviq.io.
Credibility built on verifiable architecture, not marketing claims.
Trust is earned through deterministic software enforcement, transparent methodology, and verified UK corporate accountability.
Explore Advisory & Governance MethodologyFour non-negotiable governance rules.
Progress requires independent review
Unreviewed submissions count as zero. Completion metrics only advance once independent second-line review is accepted.
Enforced Segregation of Duties
Control owners cannot approve their own assessments—enforced automatically at the platform data layer.
Mandatory remediation on failure
An inadequate control rating cannot be submitted without recording a formal finding, named owner, and remediation plan.
Immutable audit trail & advisory AI
AI extraction remains strictly advisory until human sign-off, with every decision recorded in an append-only audit log.
Submitted by Control Owner
First LineConclusion: Inadequate · Priya Raman
Returned by Second-Line Reviewer
Independent Challenge“No evidence attached and no agreed remediation plan.”
Evidence & Remediation Plan Attached
Re-SubmissionTimestamped proof & remediation milestone linked to finding
Accepted by Independent Oversight
ValidatedConclusion supported and tracked to verified closure
Speak with our architects and security specialists.
Whether you are requesting an OrviQ demonstration or scoping an offensive, defensive, or advisory engagement, our security and governance specialists respond directly.
Instant Demo AccessExplore OrviQ's pre-configured demonstration environment to inspect live regulatory requirements, control assurance maps, and risk workflows directly.
Nexa Cyber Security Limited
Co. No. 15360963Registered Head Office
220-222 Warwick Road, Sparkhill, West Midlands, Birmingham, England, B11 2NB
Enterprise & Support Email
support@nexacybersecurity.comDirect Telephone
+44 7931 975173